Is Engineering Significant Difference the Key to Enhanced Cybersecurity?

A lively conversation about whether “Engineering Significant Difference” is the key to enhanced cybersecurity.

Contributors:

Peter Davies, Security Expert operating at the convergence of Safety and Security.
An honorary Fellow with Imperial College’s Institute for Security Science & Technology and chair of the AESIN Security Workstream. He is a leading expert on Countering Cyber Attacks targeted Supply Chain infiltration and Cyber Physical Attacks. He has led the Cyber Security aspects of 3 C-CAV research activities and has 30+ years of verifying security systems in hardware and software. Peter likes to say that he does security where it can’t afford to fail. 

Professor Kerstin Eder, University of Bristol, who researches research specification, verification and analysis techniques, allowing engineers to design a system and verify/explore its behaviour in terms of functional correctness, safety, performance, power consumption and energy efficiency. Her work includes both formal methods and traditional simulation-based approaches. She has a strong background in computational logic, especially formal verification, declarative programming languages and their implentation, abstract machines, compilation techniques and meta programming.

Dr Weiqiang Liu is currently a full Professor and the Vice Dean of College of Electronic and Information Engineering, Nanjing University of Aeronautics and Astronautics (NUAA), Nanjing, China. He received the B.Sc. degree in Information Engineering from NUAA and the Ph.D. degree in Electronic Engineering from Queen’s University Belfast (QUB), Belfast, United Kingdom, in 2006 and 2012, respectively.

Dr Daniel Page is currently a Senior Lecturer within the Department of Computer Science, University of Bristol. His current research focuses on challenges in cryptographic engineering, the implementation (in hardware and/or software) of and implementation attacks (relating to both side-channel and fault attacks) on cryptographic primitives and arithmetic in particular. 

Dr. Chongyan Gu is a Lecturer in the School of Electronic Electrical Engineering and Computer Science (EEECS) at Queen’s University Belfast, and a member of the Centre for Secure Information Technologies (CSIT) within Queen’s Global Research Institute of Electronics, Communications & Information Technology (ECIT). Her research focuses on developing advanced hardware security methodologies for enhancing the robustness, reliability, resource efficiency and resilience of hardware devices. 
PhD Studentship Opportunities at Queen’s University Belfast

The Centre for Secure Information Technologies (CSIT) at Queen’s University Belfast is seeking motivated PhD students to work on the following research topics:

For further information and how to apply, please visit the QUB website for PhD study

Automotive Cyber Resilience: Operationalizing, Standards and Research

Presenting the work of AESIN and the UK Automotive Council and Zenzic, supported by Queens University Belfast, University of South Wales, University of Edinburgh and the Turing Institute and with further support from BSI, this series of workshops is designed to:

  • Present and discuss the limitations with existing standards in meeting the requirements of the Automotive and other mobility industries worldwide
  • Present the methodology proposed by AESIN, UK Automotive Council and Zenzic to achieve operationalizable and legally sustainable cyber resilience
  • In the context of that methodology set out the research agenda and give examples of applying the outcomes of existing and potential research in support of the methodology

There are 4 workshops which are each limited to 50 attendees. At each site a different academic partner will highlight examples of applying the outcomes of existing and potential research in different areas in support of the methodology.

The workshops will be held at:

4th Dec 2019 – ECIT, Queen’s University of Belfast, Queen’s Road, Queen’s Island, Belfast, BT3 9DT. QUB are the academic partner and will use research examples from hardware. Click here for tickets

11th Dec 2019 – University of South Wales Conference Centre, CF37 1DL UoSW are the academic partner and will use research examples from Forensics. Click here for tickets

8th Jan 2020 – NXP, Colvilles Road, Glasgow G75 0TG. University of Edinburgh are the academic partner and will use research examples from Modelling. Click here for tickets

15th Jan 2020 – Plexal, 14 East Bay Lane, Here East, Queen Elizabeth Olympic Park, London, E20 3BS. The Turing Institute are the academic partner and will use research examples from mathematics and probability. Click here for tickets

Who should attend?

This event is designed specifically for researchers with an interest in automotive cyber resilience and the application of security and other research outcomes, including PhD and other research students and their supervisors, early career researchers, representatives from industry, government and other defence and security-relevant NGOs.

For further information please refer to the below guide.

IEEE Computer Symposium – Miami, July 2019

Wolfe Centre

We are delighted to welcome another new guest blogger to contribute to the RISE blog for August 2019. Shichao Yu is a PhD student at Queen’s University Belfast, working in the world class research centre – The Centre for Secure Information Technology (CSIT). Thank you Shichao!

Welcome to Miami – Summer is coming!

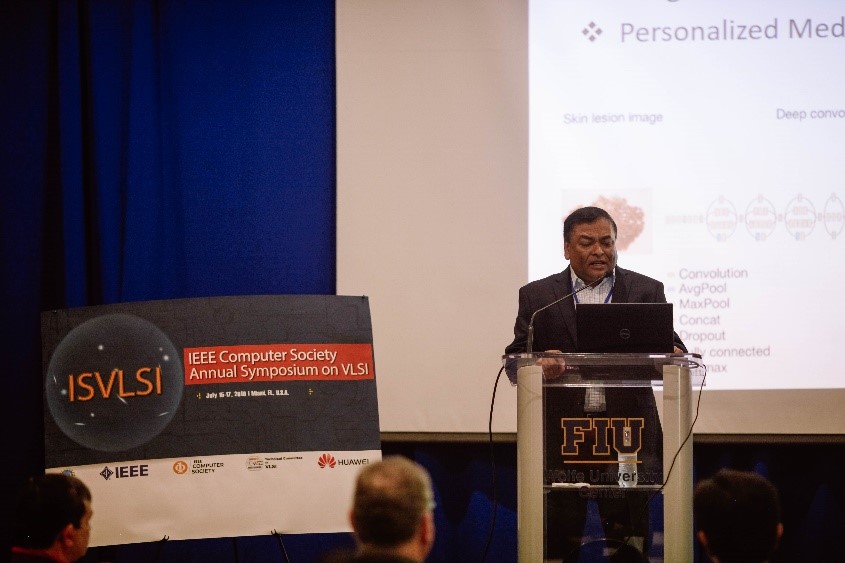
Hi, I am Shichao, I am typing this blog shortly after the closing remarks of IEEE Computer Society Annual Symposium on VLSI in Miami, which is excellent and provided me an amazing conference experience. This was my first time in Miami, and this is the first conference I have attend with a poster paper. I travelled from Belfast to Miami, from north to south, feeling like I flew into the summer from winter when I just arrived there. If I choose rainy day as the mark of the climate in Belfast, then Miami’s symbol must be sunshine.

ISVLSI 2019 @ Miami

ISVLSI is an IEEE computer society annual symposium with a history over three decades. It explores emerging trends, novel ideas and basic concepts covering a broad range of VLSI-related topics, which also include new technologies and burgeoning application areas, such as hardware security, and artificial intelligence.

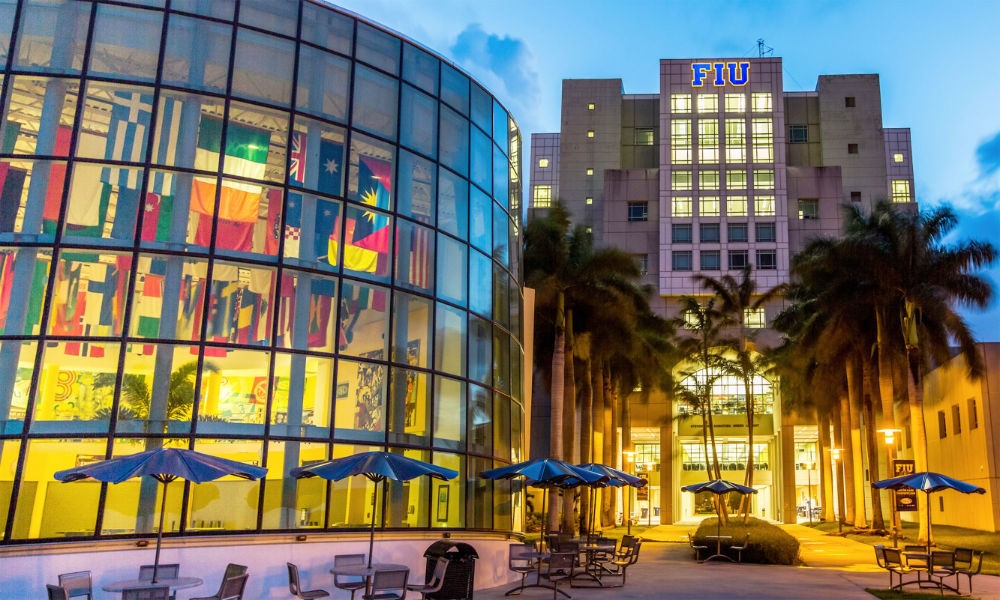
This year’s ISVLSI was held at Florida International University in Wolfe University Center.

What impressed me is that more than 25% of submissions this year related to system design and security (SDS), and the submission number occupies the first in all categories. I can see that the security direction is receiving increasing attention from researchers all over the world.

“Can you trust your machine learning system?”

For Hardware Security, the papers presented in this year’s security session mainly focused on logic obfuscation, side channel susceptibility mitigation, secure zone design on NoC (Network on Chip) and Hardware Trojan. The System Design and Security group covers four sub-sessions in three days and two related special session: “Botnet of Things: Hardware Insecurity in the IoT Era” and “Secure, Smart, Connected Devices for Emergent Applications”, which talk about IoT devices and it’s security problems.

In addition, an enlightening keynote “Can you trust your machine learning system?” presented by Professor Sandip Kundu on the second day really attracted me. This presentation showed the potential security issues of machine learning (ML) and deep learning (DL) at this stage and details the possible attack methods. As the Chinese idiom goes, virtue is one foot tall, the devil ten. It always takes constant vigilance to secure new technologies. (That scares me too Shichao!)

Poster Session

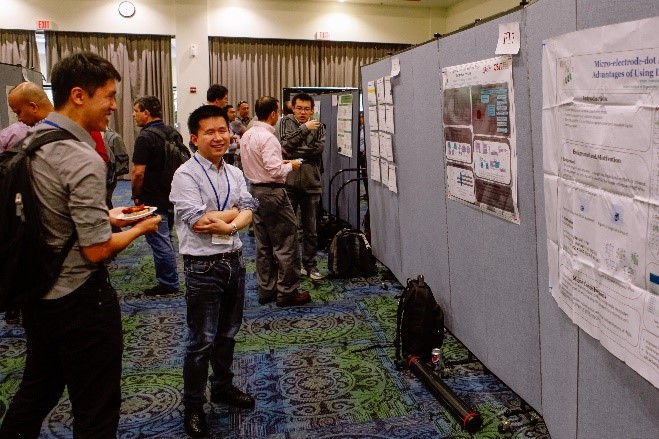
The poster session was held in the afternoon of the first day. We had a big ballroom to hang all 30 posters and 4 research demonstrations. The session last nearly two hours, which is much more than the scheduled time, with continuous technical discussions and social communication.

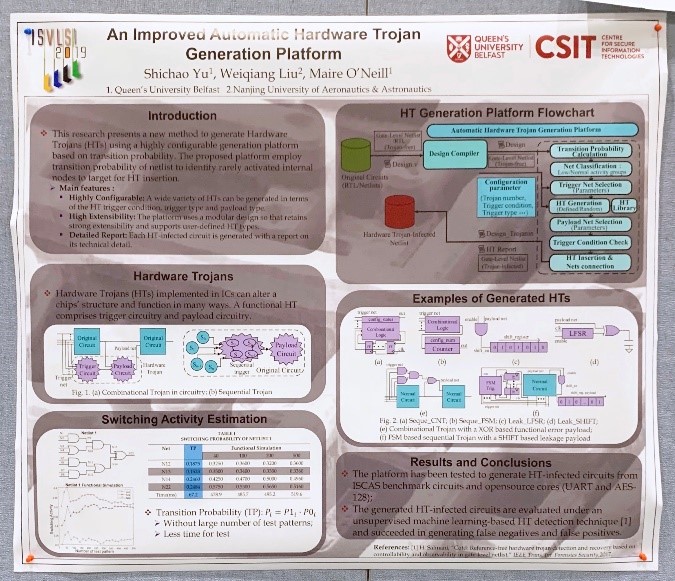
The paper I presented on my poster was “An Improved Automatic Hardware Trojan Generation Platform”, which is a new method to generate Hardware Trojans (HTs) using a highly configurable generation platform based on transition probability. (WOW :O – great stuff Shichao! \0/)

I always enjoy the discussion with other researchers. But, as I work in hardware security, I really hope that I had explained my poster clearly to some researchers who work in software side.

Until Next Time Miami 🙂

Three days ISVLSI went by too quickly and it was super busy. My record is slightly broken, but the great keynotes and presentations are unforgettable. Miami Beach is also beautiful and relaxing.

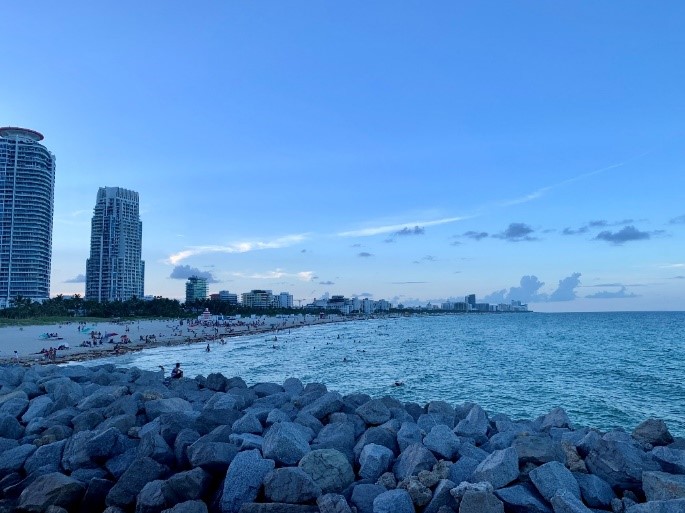
In the evening of the last day, I took a photo when blue hour made Miami Beach a little tranquil, and said goodbye to this beautiful city. (Good you got to check out the sandy beaches 🙂 BTW where is our present?? 😀 )

Miami Beach front @ dusk

End-to-End IoT Security

Our July blog post has been written by one of our Industrial Stakeholders Advisory Board (ISAB) members. A special thanks from RISE to Ilhan Gurel from Ericsson for contributing this best practice advice. Ilhan is HW and SW security expert at Ericsson.

“Security baked in at every layer, not later”

Securing entire end to end IoT chain covers securing IoT devices, backends and everything in between as well as life cycle starting from manufacturing and deployment to disposal.

Every component in this chain may have different attack surfaces, different adversaries and may be managed by different entities. It is also important to note that securing IoT devices and their backends is not an easy task and depends on operational environments, deployment models, use cases, adversaries, assets to protect and costs. No matter what these can be, there must be an adequate level of security baked into every layer and component, starting from the very beginning e.g. design phase but not added later.

The IoT Recipe for Security

Securing IoT end to end chain starts with security threat modeling and risk assessment. This is a crucial phase to find answers to security threats, mitigations and security requirements. Then it requires the following ingredients when and where applicable:

  • Hardware (HW) and Software (SW) supply chain security:
    • vulnerability and incident management
    • HW and SW components free of trojans/malwares
    • Keeping track of 3rd party HW & SW components and their origins.
  • HW Security:
    • secure boot
    • TRNG
    • secure storage
    • HW based RoT (Root of Trust)
    • HW based security features to mitigate ROP/JOP like attacks
    • HW based crypto modules
    • HW (and SW) based mitigations for side channel attacks if applicable
  • SW Security:
    • security hardening of OS and applications
    • minimal OS (including disabling/removing unsecure services/components)
    • sandboxing
    • least privileged processes
    • code signing
    • access control
    • secure SW development
    • auditing and logging
  • Trusted identities:
    • unclonable
    • unique
    • cryptographically random and strong enough during the lifetime of devices
    • generating, provisioning and storing identities securely
  • Life Cycle & Device Management:
    • secure SW updates
    • remote attestation
    • secure disposal of user and device data
  • Anomaly detection:
    • on device and at network level
  • Identity Management:
    • managing identity life cycles
    • revocations
    • renewals
    • bootstrapping
    • integration with PKI systems
  • Secure communication:
    • data confidentiality , integrity and origin in transit
    • the use of strong ciphers and mutual authentication
    • the use of secure protocols e.g. TLS/DTLS according to the best security practices as defined in RFC 7925, RFC 7525 and RFC 7540
    • the use of TLS 1.3 when and where possible. TLS 1.3 as standardized in RFC 8446 has significant security and privacy improvements comparing to TLS 1.2

How to measure security?

Connectivity also plays a crucial role with respect to high availability, battery life, reliable communication, data transmission rates (e.g. important for SW updates and rapid patching), built-in security.

Then an important question remains: how to measure security? In-house and independent security audits and reviews, security certifications are all relevant and may be one of the answers.

Securing end to end IoT chain is a not easy task but it is achievable. It requires all the ingredients mentioned above when and where applicable, most importantly security awareness of end users, device owners, manufacturers, platform and service providers, HW and SW developers, and more.